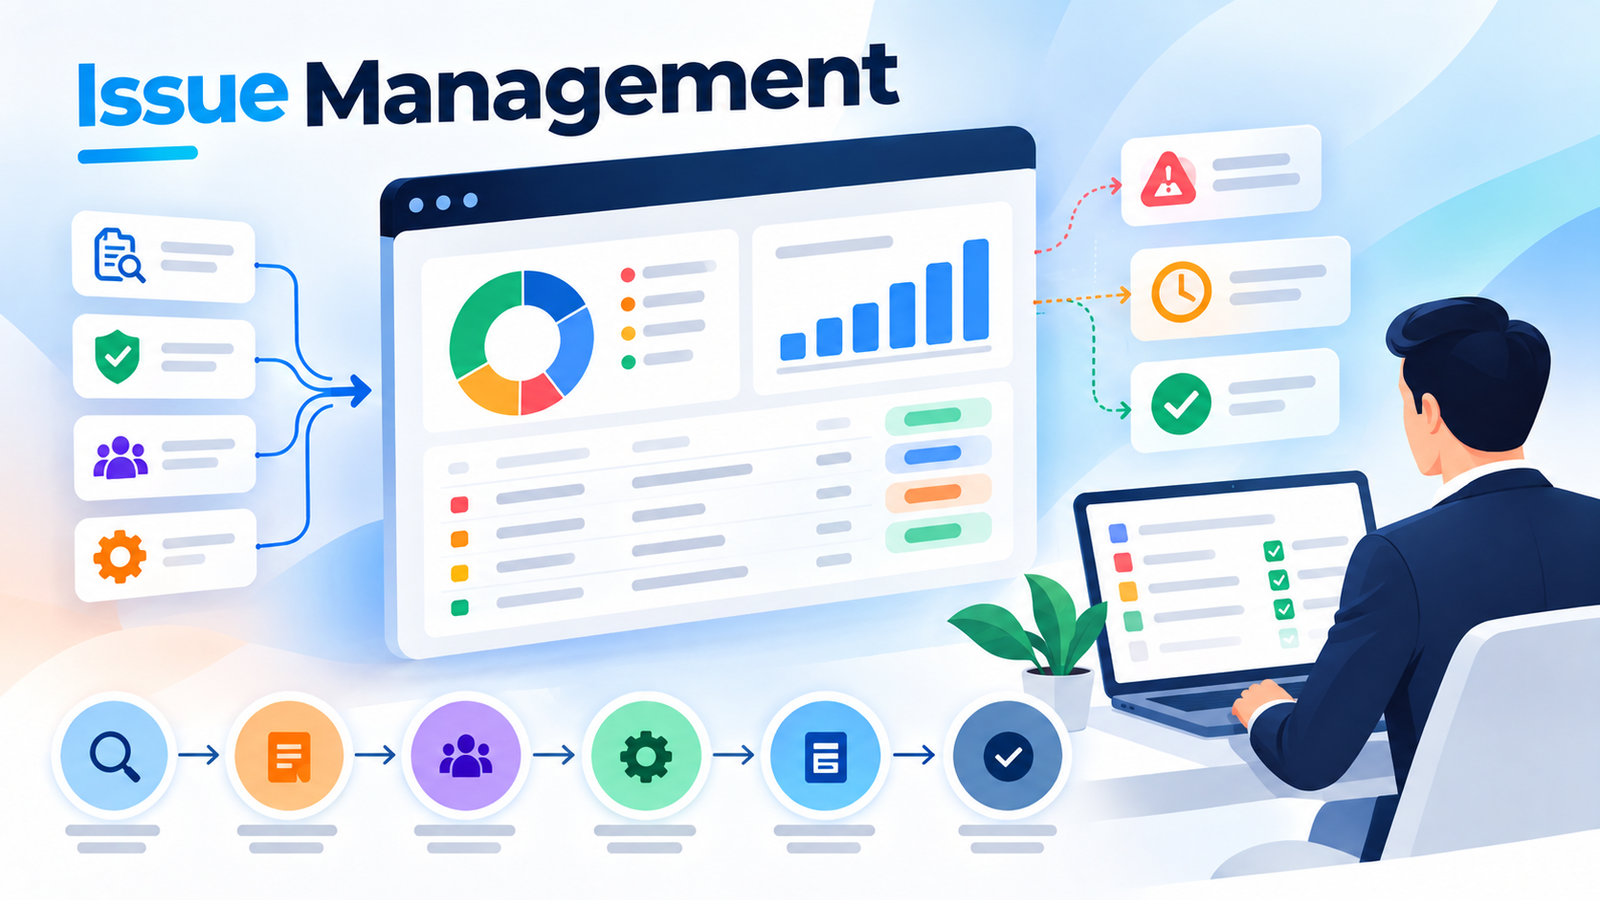
Introduction An organization can identify hundreds or thousands of problems across internal audits, risk assessments, compliance reviews, control testing, cybersecurity assessments, vendor reviews and regulatory examinations. Identifying those problems is only the beginning. The harder questions are: Who owns the issue? How serious is it? What caused it? What must be fixed? When must remediation...