
Introduction
Organizations routinely encounter situations where a policy, control, security requirement, compliance obligation, or established standard cannot be met as defined. These deviations may be necessary, but managing them through email approvals, spreadsheets, or informal requests can create governance gaps.
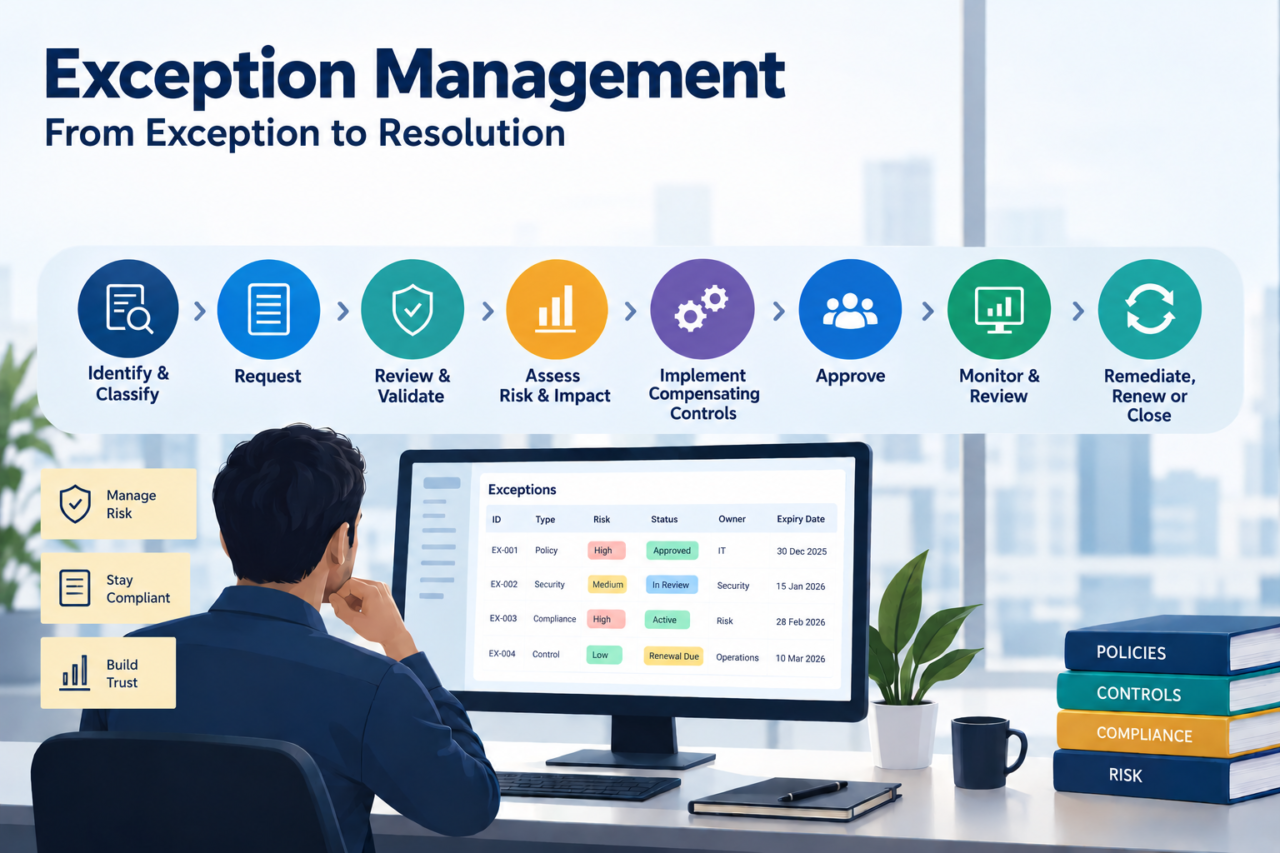
An exception management process provides a structured way to identify, request, assess, approve, monitor, review, and close exceptions while maintaining clear ownership, accountability, and audit-ready evidence.
Exceptions should be treated as controlled and time-bound governance decisions, not informal workarounds. A well-designed process helps organizations answer critical governance questions:
- Why was the exception requested?
- Which policy, control, or requirement is affected?
- What risk does the deviation create?
- Who evaluated and approved it?
- What compensating controls are in place?
- When does the exception expire?
- Has the exception been reviewed or remediated?
What Is an Exception Management Process?
An exception management process is a defined governance workflow used to identify, document, assess, approve, monitor, review, and close deviations from established policies, controls, standards, or requirements.
The objective is not to eliminate every exception. Instead, the objective is to ensure that every approved exception is justified, risk-assessed, owned, authorized, time-bound, monitored, supported by evidence, and closed or formally renewed.
Why Is Exception Management Important in GRC?
The risk is not the exception itself; the governance risk comes from exceptions that are undocumented, unowned, unassessed, or allowed to remain active without review.
Without a formal exception management process, organizations can lose visibility over policy deviations and accepted risks.
Exception Management Process: 8 Key Steps
Identify and Classify the Exception
The process begins when a business, security, compliance, or control owner identifies a situation where an established policy, control, standard, or requirement cannot be met as defined.
Before submitting the request, classify the exception according to its nature and potential impact. Common categories include policy, security, compliance, operational, and control exceptions. This initial classification helps determine the appropriate risk assessment, approval authority, review requirements, and monitoring approach.
Submit the Exception Request
The request should clearly define the affected requirement, reason for the deviation, business justification, scope, requested effective date, review date, expiry date, owner, initial risk information, and supporting evidence.
Typical information: Exception type, policy affected, business justification, reason, systems affected, effective date, review date, expiry date, business impact, initial risk assessment, proposed compensating controls, supporting evidence, exception owner.
Review and Validate the Request
The relevant risk, compliance, security, or business function reviews the request to determine whether the exception is justified and sufficiently documented.
Key validation questions: Is the exception genuinely required? Is the affected requirement correctly identified? Is the business justification adequate? Is the requested duration reasonable? Has the same exception already been approved elsewhere? Can the requirement be met through an alternative solution?
Perform Risk and Impact Assessment
Every material exception should be evaluated based on the risk created by the deviation. The assessment should determine the level of residual risk that remains after existing and proposed controls are considered.
Assessment factors: Likelihood and potential impact, data sensitivity, system criticality, security implications, regulatory impact, duration, existing controls, residual risk.
Assess and Implement Compensating Controls
Where appropriate, compensating controls should be identified, implemented, and evaluated to determine whether they adequately reduce the exposure created by the exception.
Examples: Additional monitoring, increased review frequency, manual approval controls, restricted access, additional logging, network restrictions, temporary procedural controls.
Route the Exception for Approval
Approval authority should be determined by predefined risk thresholds rather than applied uniformly to every exception. Exceptions should be routed to an approval authority appropriate to their risk and business impact.
Approval levels (example): Low-risk exceptions may be approved by the relevant business or control owner, while moderate- and high-risk exceptions may require progressively higher Risk, Compliance, Senior Management, CISO, or other designated authority approval, depending on the organization’s governance model.
Monitor and Periodically Review the Exception
Approval does not mean the exception can be forgotten. Once approved, the organization should monitor current status, exception owner, expiry date, review date, compensating controls, remediation progress, changes in risk, evidence, and business conditions.
Exceptions should also be reassessed when there is a material change in the underlying risk, system, control environment, business process, or regulatory requirement.
Remediate, Renew, or Close the Exception
Before an exception reaches its expiry date, determine the appropriate outcome:
Remediate: The underlying issue has been resolved and the original requirement can now be met.
Renew: The exception remains necessary and requires a new approval based on its current risk and business justification. Renewal should not be treated as an automatic extension.
Close: The exception is no longer required, applicable, or justified.
Exception Management Lifecycle
↓
↓
↓
↓
↓
↓
↓
Types of Exceptions in GRC
Policy Exceptions
Temporary deviations from internal policies or standards.
Security Exceptions
Deviations from security requirements, controls, or technical standards.
Compliance Exceptions
Approved deviations relating to compliance requirements or control obligations.
Requests where an organization seeks formal authorization to accept residual risk.
Control Exceptions
Deviations where an established control cannot be implemented or operated as required and an alternative control arrangement may be necessary.
Operational Exceptions
Temporary deviations caused by operational, technical, business, or process constraints.
Exception Management vs. Risk Acceptance
An exception governs the deviation; risk acceptance governs the decision to accept the resulting residual risk.
What Should an Exception Record Contain?
Common Exception Management Challenges
Spreadsheet-based tracking
Spreadsheets can provide basic visibility but become difficult to maintain when exception volume, ownership, approvals, and expiry dates increase.
Email-based approvals
Email makes it difficult to maintain a consistent approval workflow and centralized audit trail.
No expiry governance
Exceptions without defined expiry and review dates can become permanent control gaps.
Inconsistent approval
Different teams may apply different standards when evaluating similar exceptions.
Poor ownership
Without a clearly accountable owner, remediation and renewal activities can stall.
Limited evidence
When requests, approvals, assessments, and supporting documents are distributed across systems, audit preparation becomes more difficult.
Exception Management Best Practices
Exception Management Metrics and KPIs
How GRC Technology Improves Exception Management
How ASPIA Operationalizes Exception Governance
ASPIA operationalizes this lifecycle through structured exception workflows that bring exception governance into the broader GRC operating model.
Request
Structured exception intake to capture business justification, requirement, risk context, ownership, and supporting information.
Assess
Risk and impact evaluation, with compensating controls incorporated into the governance process.
Approve
Configurable, multi-level approval workflows route exceptions to appropriate stakeholders based on governance requirements.
Monitor & Review
Active exceptions tracked by ownership, status, expiry, and review requirements, with notifications and escalations supporting timely action.
Renew, Remediate, or Close
Renewal/reapproval, remediation, and closure while maintaining the associated governance record and audit trail.
Frequently Asked Questions
Conclusion
A mature exception management process ensures that policy, control, security, and compliance deviations are handled as deliberate governance decisions rather than informal workarounds.
The strongest processes combine structured requests, risk-based assessment, appropriate approval, compensating controls, clear ownership, time-bound monitoring, renewal governance, remediation, and complete evidence.
When these activities are connected to the wider GRC environment, organizations gain better visibility into where exceptions exist, why they were approved, how much risk they introduce, and whether they are being resolved.
Operationalize Your Exception Governance with ASPIA
Structured workflows for exception requests, assessments, approvals, monitoring, renewals, and closure—bringing exception governance into the broader GRC operating model.

